
The enterprise AI rush leaves product teams scrambling to ship features fast and answer questions later. Building ethical and responsible AI into software is no longer optional—it is a core survival metric. Enterprise buyers demand strict data privacy, robust risk management, and transparency before signing contracts. Ignoring these expectations exposes brands to liabilities under mandates like the EU AI Act and GDPR.
Core Pillars of Responsible AI in B2B
Deploying responsible AI in B2B ecosystems requires moving past vague manifestos. Modern software architecture demands technical safeguards that guarantee accountability without crippling innovation.
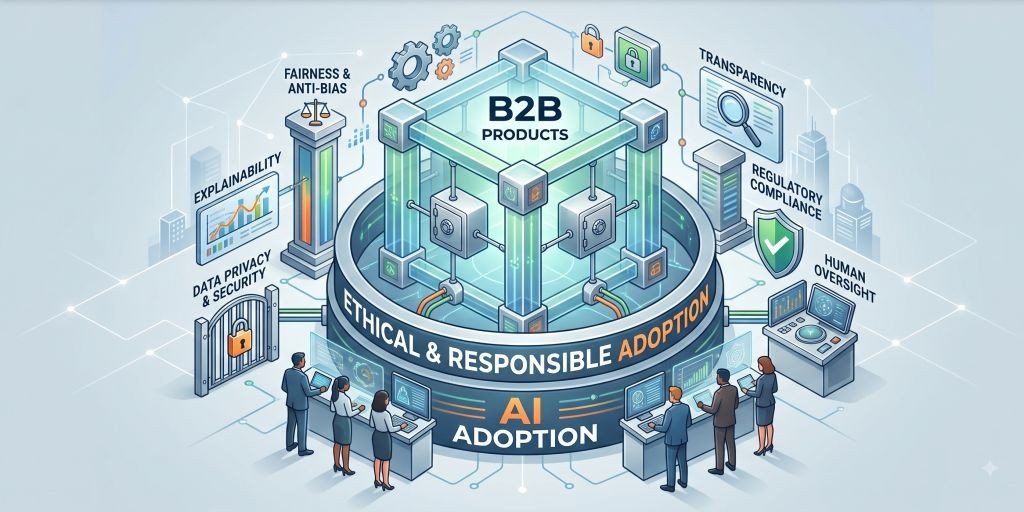
- Explainable AI (XAI): Black-box neural networks generate pushback from legal teams. Vendors must provide clear audit trails showing how models reach predictions.
- Fair Machine Learning: Training datasets often reflect historical biases. Data hygiene prevents models from perpetuating systematic errors in software.
- Data Privacy and Security Standards: Proprietary customer data should never feed shared public models. Zero-data-retention architectures protect enterprise IP.
- Continuous Model Auditability: Generative tools introduce attack vectors like prompt injection. Enterprise defenses require real-time threat monitoring and patching.
Risks of Unchecked AI Integration
What happens when teams rush models into production without oversight? Hallucinations ruin customer trust overnight, while biased decision engines invite regulatory penalties. Algorithmic drift degrades product performance over time, eroding user confidence. Enterprise clients walk away the moment they suspect their data might leak into public training pools. Does shipping fast matter if it destroys buyer confidence? Not really.
Step-by-Step Framework for Ethical AI Adoption
Scaling enterprise AI compliance takes deliberate engineering rather than casual policy memos.
- Step 1: Establish an internal AI governance framework. Assemble a board featuring engineering, legal, and product leads to define risk thresholds and workflows.
- Step 2: Audit training data sources for compliance and bias. Scrutinize datasets for copyrighted content, personal identifiers, and skewed distribution before training algorithms.
- Step 3: Implement human-in-the-loop (HITL) checkpoints for high-stakes decisions. Keep human experts in the loop for high-risk automated actions, ensuring accountability.
- Step 4: Conduct regular security and vulnerability assessments. Run continuous penetration tests, red-teaming, and automated checks to detect model exploits.
Building trustworthy AI solutions requires talent that understands machine learning mechanics and compliance landscapes. When product leaders hire AI developers from partners like Beetroot, they gain engineers who integrate safety directly into the codebase. Responsible engineering is the ultimate competitive advantage.

Chris Mcdonald has been the lead news writer at complete connection. His passion for helping people in all aspects of online marketing flows through in the expert industry coverage he provides. Chris is also an author of tech blog Area19delegate. He likes spending his time with family, studying martial arts and plucking fat bass guitar strings.